



Capture Activity
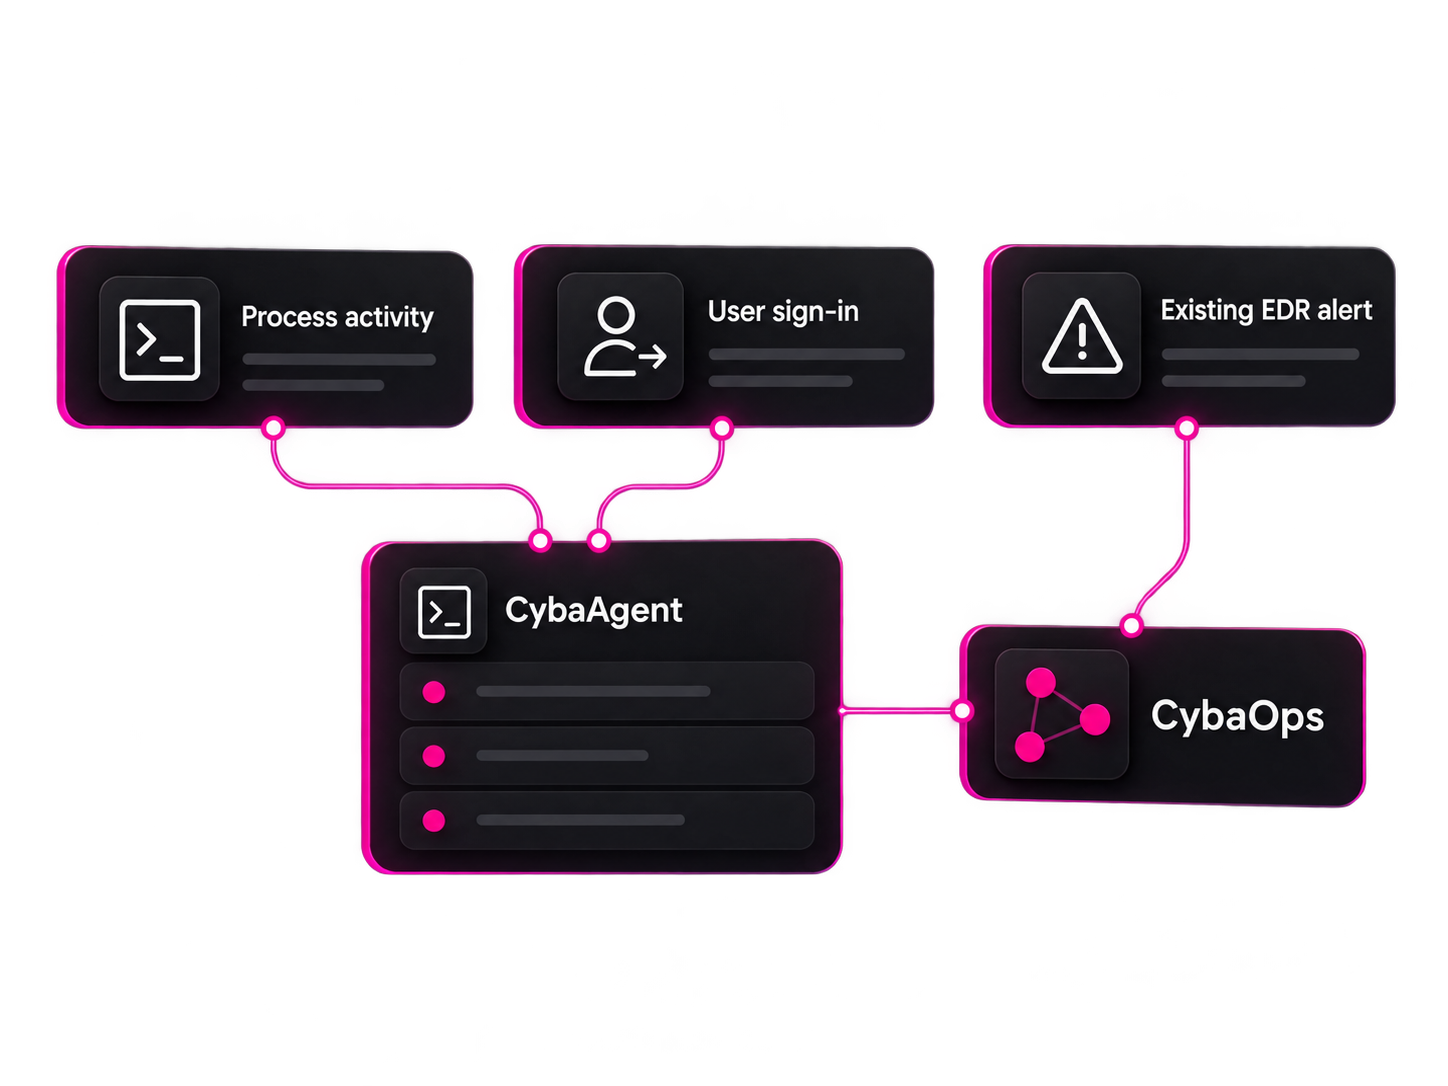
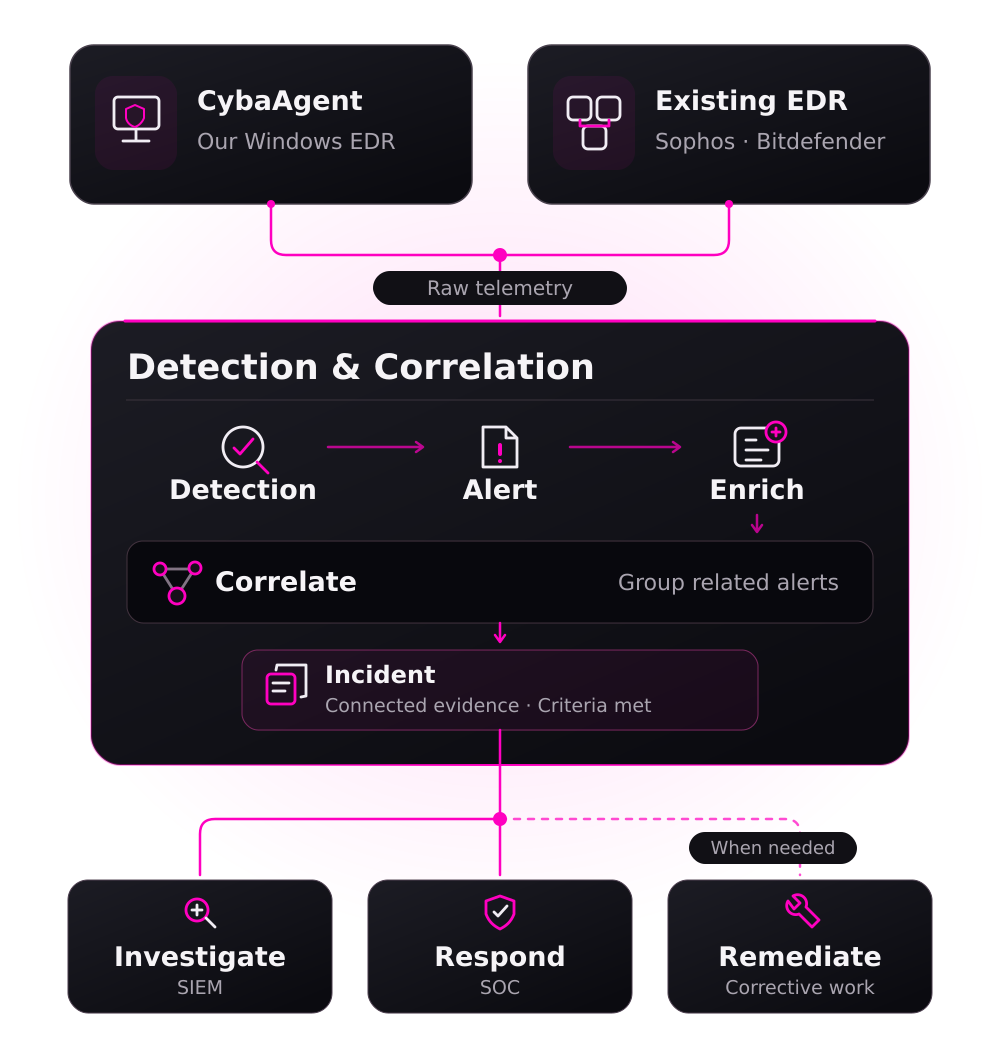
CybaAgent brings Windows endpoint activity into CybaOps. Connected EDR tools can contribute their own security findings too.

Detect Relevant Behaviour
Detection rules evaluate incoming events for suspicious or security-relevant activity. Matches become alerts, enriched with available asset, identity and threat context.

Connect the Findings
The correlation engine assesses related alerts together. Rule conditions, time windows and scores help determine when activity warrants an incident.

Investigate and Respond
Qualifying activity becomes an incident with supporting evidence, giving our SOC the context to investigate and coordinate the appropriate response.


Behavioural Detection

Connected Security Signals
Bring endpoint findings into the wider investigation. Related alerts can be assessed around a common device or identity, helping our SOC understand why they matter together.

Context for Prioritisation
The importance of a finding depends partly on what it affects. Available asset and identity information helps put detections in context and supports prioritisation.

Evidence Behind the Incident
Keep the findings that explain why an incident was raised. Contributing alerts, affected assets and source evidence support investigation and make the decision easier to understand.
"We have increased our internal security knowledge across the organisation and especially in IT and engineering. This has allowed us to bring some services in-house and substiture those with more advanced external services."


1
What is Endpoint Detection & Response (EDR)?
Endpoint detection and response (EDR) monitors activity on devices such as laptops, desktops and servers to identify suspicious behaviour and support investigation and response.

2
What is CybaAgent?
CybaAgent is CybaVerse’s own EDR agent for Windows devices. It brings endpoint activity into CybaOps for detection, correlation and investigation.

3
Can we keep our existing EDR tools?
Yes. You can run your existing EDR alongside CybaAgent and integrate supported security signals into CybaOps. This allows tools such as Sophos and Bitdefender to remain part of your security setup.
4
How does CybaOps decide which alerts become incidents?
CybaOps evaluates alerts against correlation rules. These can consider related activity, affected devices or identities, scores and defined time windows. An incident is created when the relevant promotion criteria are met.
5
What's the difference between EDR and MDR?
EDR provides endpoint detection and response technology. Managed detection and response (MDR) adds a service that monitors, investigates and responds to security activity. CybaAgent provides endpoint capability within CybaVerse’s managed security offering.