Security Assessments Built

Around Real Risk

Know Your Security Gaps Before Attackers Find Them

Most organisations don't have a clear picture of their cyber security posture. They have tools, policies and processes,  but no structured way to measure how well those controls work. CybaOps gives you that picture.

What Is a Cyber Security Assessment?

A cyber security assessment is a structured evaluation of an organisation's existing security controls, processes and technologies. It identifies gaps between current practice and recognised security standards, helping organisations understand where they are exposed and where to focus improvement efforts.

Assessments vary in form. Some are consultant-led engagements. Others are automated scans. The CybaOps Security Assessment is a guided self-assessment: the organisation's own team answers a set of structured questions, and the platform grades the responses against an established framework.

Assess. Prioritise. Improve.

Helping Organisations Quickly Idenitfy Gaps In Their Posture

The CybaOps Security Assessment takes you through 50 straightforward questions based on theNCSC's 10 Steps to Cyber Security, helping you quickly understand where your security is strong and where there are gaps are all in a clear format so you know what needs your attention.

The 10 NCSC Categories Covered:

Group 1707480970-1
Risk Management

How cyber risk is identified, assessed and managed.

Engagement and Training

Staff awareness, training and overall security culture. 

Asset Management

Visibility and control across organisational assets. 

Architecture and Configuration

Secure system design, configuration and hardening. 


Data Security

Protection of sensitive and business-critical information. 

Vulnerability Management

How weaknesses are identified, prioritised and addressed. 

Identity and Access Management

How user access is controlled and monitored. 

Logging and Monitoring

Visibility into security activity, detection and audit trails. 

Incident Management

Preparedness to detect, respond to and recover from incidents. 


Supply Chain Security

Managing security risk across suppliers and third parties. 


What You Receive Once 

Once the assessment is complete, CybaOps provides:

  • An overall cyber security achievement grade reflecting your organisation's posture across all 10 categories

  • Individual category grades showing where controls are strong and where gaps exist

  • Best-practice guidance for each section, so you know what good looks like and what steps to take next

  • A downloadable Security Assessment report suitable for internal review, management reporting, or governance discussions

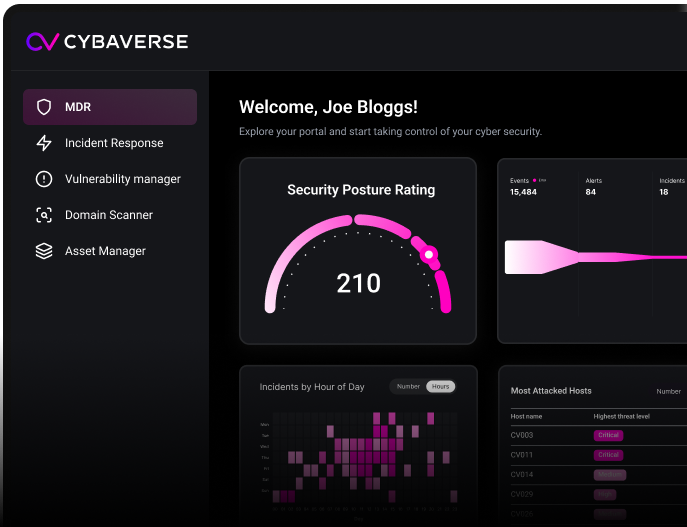
  • Input into your CybaOps Security Posture Rating, the platform's live view of your overall security position

Website Cards (1200 x 898 px) (3)

Real-Time Security Position Indicator

CybaOps brings together your assessment responses with data from across the platform, including vulnerability management, to give you a clearer picture of your overall security posture.

Rather than giving you a score that sits still until the next assessment, your posture updates as your environment changes and risks are addressed.


How this works in practice:


Complete or update the Security Assessment to reflect your current controls and processes

New vulnerabilities identified through CybaOps can affect your posture rating even if your assessment answers remain unchanged

Resolving vulnerabilities and addressing security gaps improves your overall rating over time

The result is a continuously updated view of security posture, not a point-in-time snapshot that goes stale
A Practical Benchmark for Your Security Posture 

The NCSC’s 10 Steps to Cyber Security provides a recognised framework for managing cyber risk across UK organisations.

By aligning the CybaOps Security Assessment to it, your results are measured against a practical, established security baseline. 


  • Recognised by UK regulators and government bodies
  • Applicable across sectors, from financial services and healthcare to technology and professional services
  • Practical and actionable, focused on controls that can be implemented rather than theoretical ideals
  • Regularly updated by the NCSC to reflect the current threat landscape
Frame 1

 Frequently Asked Questions 

1 Is the Security Assessment the same as a penetration test?

No.

A penetration test actively attempts to exploit vulnerabilities in your systems to identify weaknesses.

The CybaOps Security Assessment is a self-assessment: your team answers structured questions about your existing controls and processes.

The two serve different purposes and should be used alongside each other, not interchangeably.

2 How long does the Security Assessment take to complete?

The assessment contains 50 multiple-choice questions across 10 categories.

Progress is saved automatically, so it can be completed in a single session or across multiple sessions. Most organisations complete it in under an hour.

3 Can we retake the assessment as our security posture changes?

Yes.

Selecting Retake Assessment within CybaOps preserves your existing answers while allowing you to review and update them.

Once resubmitted, the platform generates an updated score.

CybaVerse recommends reviewing the assessment regularly, particularly when security controls, technologies, or processes change.

4 Does the Security Assessment contribute to our Security Posture Rating?

Yes.

The assessment is one of several inputs into the CybaOps Security Posture Rating. Other platform data, including vulnerability management information, also influences the rating.

This means your posture rating can change even between assessment submissions.

5 Who should complete the Security Assessment?

The assessment is designed to be completed by the person or team responsible for cyber security within the organisation.

This is typically an IT manager, security manager, or CISO.

For the results to be meaningful, answers should reflect the organisation's actual current controls rather than aspirational or planned improvements.

Want To Know How We Control Chaos?

Talk to the CybaVerse team to understand how CybaOps and the Security Assessment can work for your organisation.

Address

Suite C, Building 2000, Lakeside North Harbour, Portsmouth, PO6 3EN