Identity Threat Detection & Response (ITDR)

Protect your business from compromised accounts and identity misuse, with monitoring and investigation from our Cyber Operators and clear visibility through CybaOps.

What is Identity Threat Detection and Response?

Identity Threat Detection and Response (ITDR) helps spot and respond to compromised accounts and misuse of access, protecting the identities that connect people to business systems and information.

CybaOps integrates with your supported identity provider and brings account activity into your wider security operation. Identity protection, investigation and response come together in one platform.

Intelligent Detection. Expert Response.

CybaOps analyses identity activity to detect threats and connect related signals, giving our Cyber Operators the context to act when a threat is identified.

Our Operators then investigate what happened, establish which accounts are affected and determine the response needed. Findings, response actions and outstanding remediation work remain visible through CybaOps.

A Valid Login Can Still Put Your Business At Risk

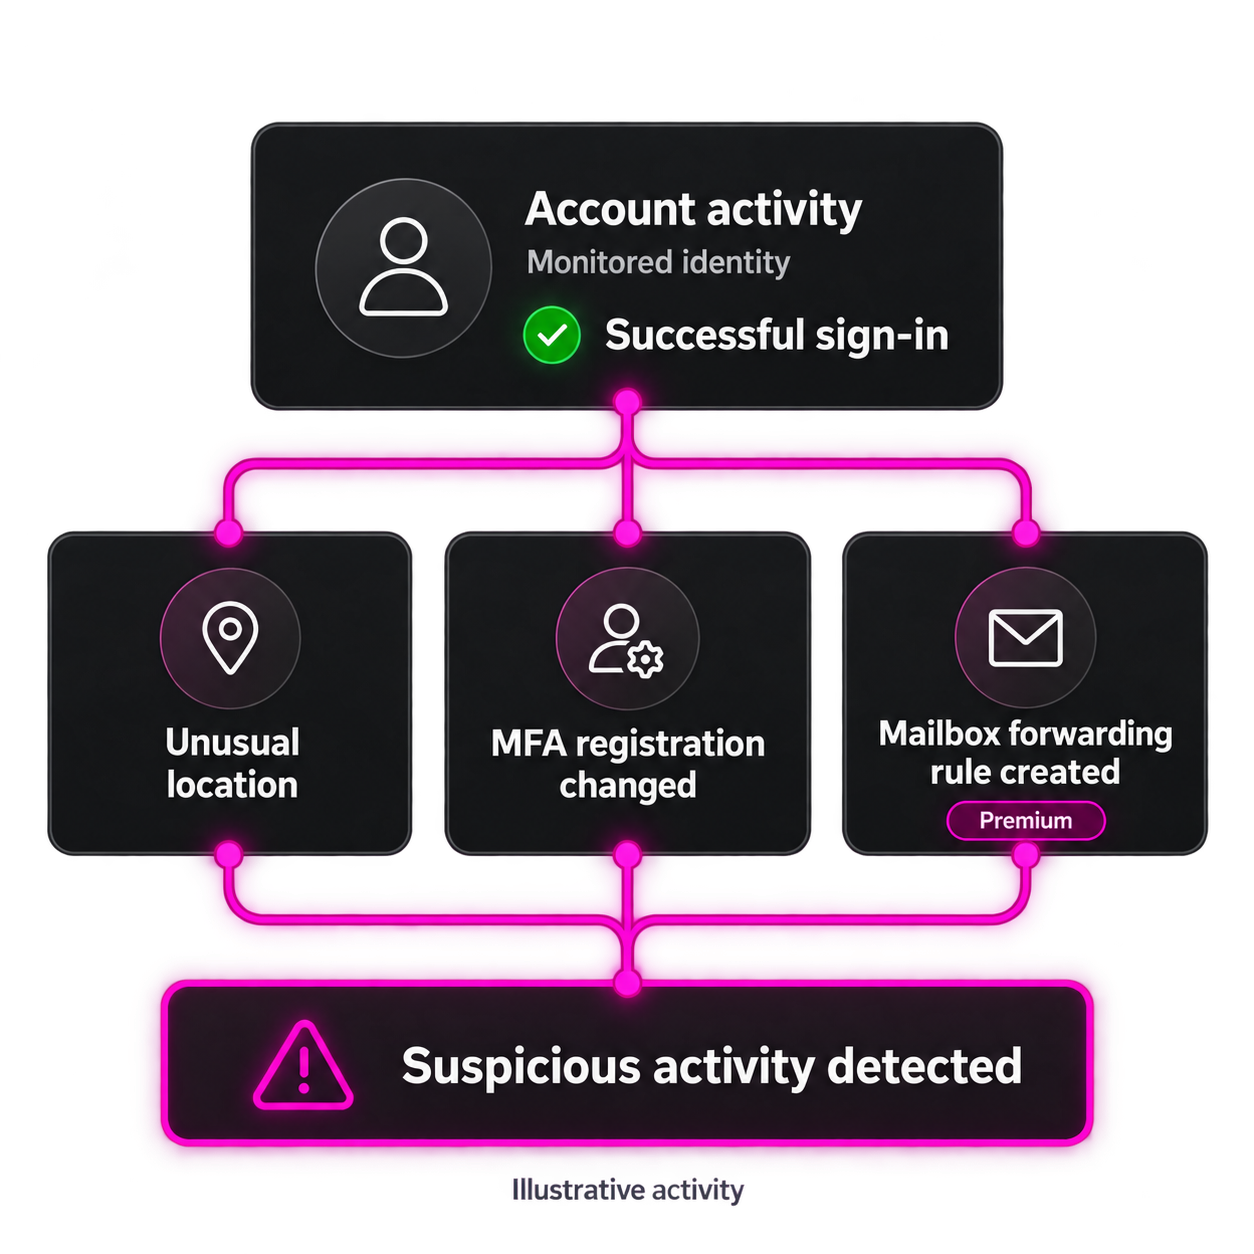
A compromised account can give an attacker access to emails, applications and sensitive information without deploying malware. Once inside, they may change permissions, create mailbox rules or use the account to make convincing requests to colleagues and customers.

The challenge is recognising when apparently legitimate access is being misused. A successful sign-in only tells you that access was granted. It does not tell you whether the person using the account should be there.

CybaVerse helps identify the activity that deserves attention, investigate what happened and track the work to address the risk. Identity protection becomes part of your wider security operation, with visibility through CybaOps.
Account activity branching alert map

Identity Protection Built Into Your MDR Service

CybaCore includes ITDR. CybaEdge and CybaOne include ITDR Premium for deeper Microsoft 365 visibility and endpoint context.
ITDR

ITDR

Included with CybaCore

Monitor suspicious access and identity changes through Microsoft Entra ID.

  • Password spraying and brute force attempts
  • Impossible travel and unusual-country sign-ins
  • Attempts to access disabled accounts
  • Privileged role and MFA registration changes
  • New guest accounts and legacy authentication usage

Data sources: Microsoft Entra ID sign-in and audit logs.
ITDR Premium

ITDR Premium

Included with CybaEdge and CybaOne

Everything in ITDR, plus broader monitoring across Microsoft 365, email and connected endpoint activity.

  • Suspicious mailbox logins, rules and permission changes
  • Business email compromise indicators
  • Suspicious application consent and privilege escalation
  • Session anomalies and attacks targeting multiple identities
  • Identity threats connected with endpoint alerts

Additional data sources: Microsoft 365 and Exchange Online audit logs, plus EDR alerts.

Follow the Investigation Through CybaOps

CybaOps brings identity protection into your wider security operation, giving you visibility of:

  • What was detected: identity alerts and affected accounts.
  • What it connects to: related activity, correlated incidents and investigation findings.
  • What happens next: response actions and remediation progress.

Alongside Microsoft cloud monitoring, CybaVerse also detects identity threats through EDR in on-premises environments. Coverage depends on the monitored devices, supported EDR and available data.

Hear From Those That Live It

"We have increased our internal security knowledge across the organisation and especially in IT and engineering. This has allowed us to bring some services in-house and substitute those with more advanced external services."
David Halsey
CTO
"CybaOps has given us a central platform for vulnerability management alongside access to a dedicated SOC team through its MDR and ITDR services. This gives us confidence that our clients' environments are being actively monitored and that potential threats are being identified and responded to quickly."
George M
Head of Client Technical Strategy

 Frequently Asked Questions 

1 Do we need ITDR if we already use MFA?

MFA helps secure access. ITDR complements it by detecting suspicious account activity and changes to authentication or permissions, including MFA registration changes.

2 What is the difference between ITDR and EDR?

ITDR monitors accounts and access. EDR monitors devices. ITDR Premium connects identity threats with endpoint alerts to support investigation.

3 Can ITDR help detect business email compromise?

ITDR Premium monitors suspicious mailbox activity, including logins, forwarding rules and permission changes that may indicate compromise.

4 Does CybaVerse monitor Microsoft 365 identities?

Yes. ITDR monitors Microsoft Entra ID sign-in and audit logs. ITDR Premium adds Microsoft 365 and Exchange Online audit logs, alongside endpoint alerts, for broader visibility.

5 What will we see in CybaOps?

You can view identity alerts, affected accounts, related incidents, investigation findings and remediation progress. ITDR Premium also connects identity threats with relevant endpoint activity.

6 Does your identity protection cover on-premises environments?

CybaVerse also detects identity threats through EDR on monitored devices in on-premises environments. The available coverage depends on your EDR deployment and data sources, which we’ll review when scoping the service.

Know Who’s Behind the Login.

A valid login doesn’t guarantee legitimate access. Get the visibility to spot suspicious activity and the support to act on it.

Talk to our team about protecting your accounts with ITDR, backed by our Cyber Operators and connected through CybaOps.